Roles and permission model
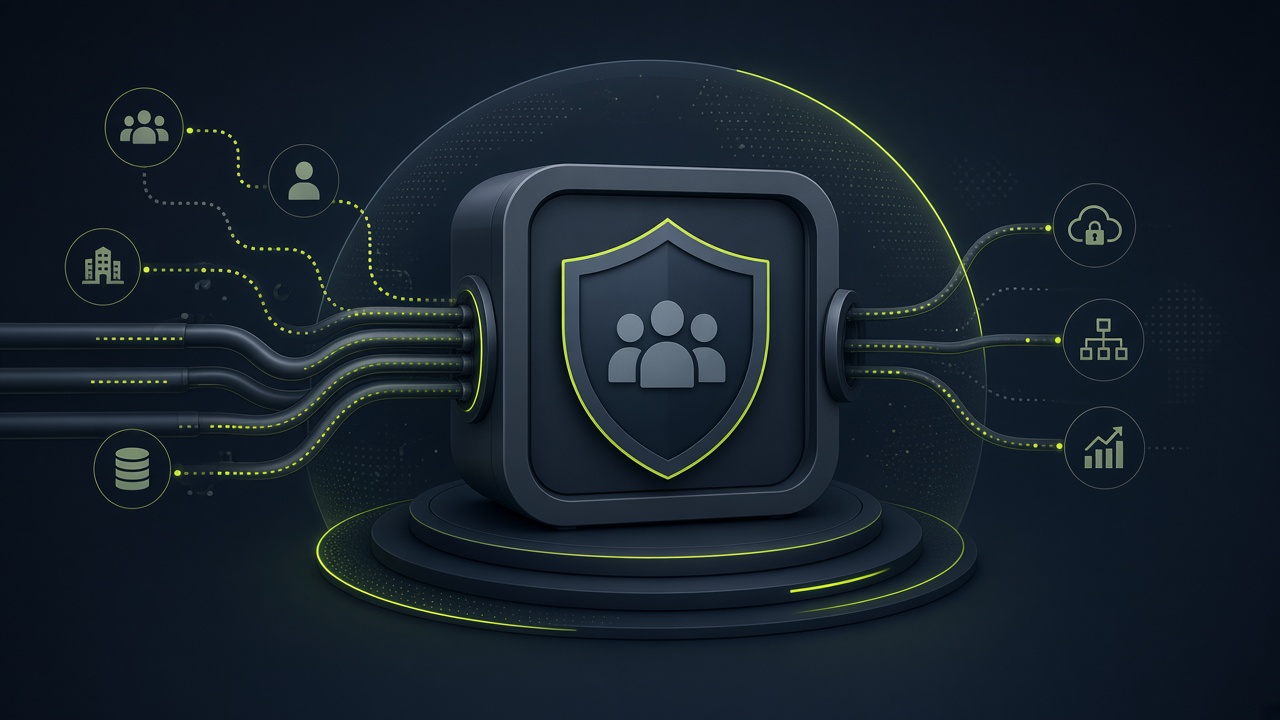
A user has an account. A role is a named set of permissions: read, write, approve, export, grant administration. A permission is checked at the boundary: screen, action or data scope (own records, a department, the whole set — by the process). One person may hold several roles when the model says so. A role is not an opinion in a spreadsheet: the system refuses an operation the role does not have. The dictionary of roles and permissions is set before build; the next role or a new data scope is a later stage.